In our hyper-connected digital landscape, Two-Factor Authentication (2FA / OTP) has become an essential shield safeguarding everything from personal email accounts and social networks to developer keys and financial assets. Yet, many modern authenticator apps have grown increasingly bloated: mandating cloud account synchronizations, requesting persistent network connectivity, pushing ad banners, or surreptitiously harvesting telemetry.
At KD Labs, we paused to ask an uncompromising question:
“Does a tool guarding your most critical cryptographic keys truly need an internet connection and telemetry tracking?”
Our definitive answer is No. That conviction led to the inception of Simple OTP.
1. The Kanso Philosophy: Simplicity in Design, Peace in Mind
Drawing inspiration from the Zen aesthetic principle of Kanso (Simplicity), Simple OTP is purposefully sculpted to strip away cognitive noise. There are zero cumbersome login rituals, zero intrusive ad popups, and zero recurring subscription prompts.
The visual palette takes cues from Japanese handmade Washi paper and charcoal Sumi ink, harmonized with warm Zen Orange accents. Every interaction is designed to evoke serenity, letting you retrieve tokens effortlessly in seconds without feeling rushed or overwhelmed.
2. Zero-Network Architecture: 100% Offline by Design
The strongest privacy pledge is one that is technically incapable of being compromised.
Inside the AndroidManifest.xml of Simple OTP, the network communication permission (android.permission.INTERNET) has been entirely eliminated:
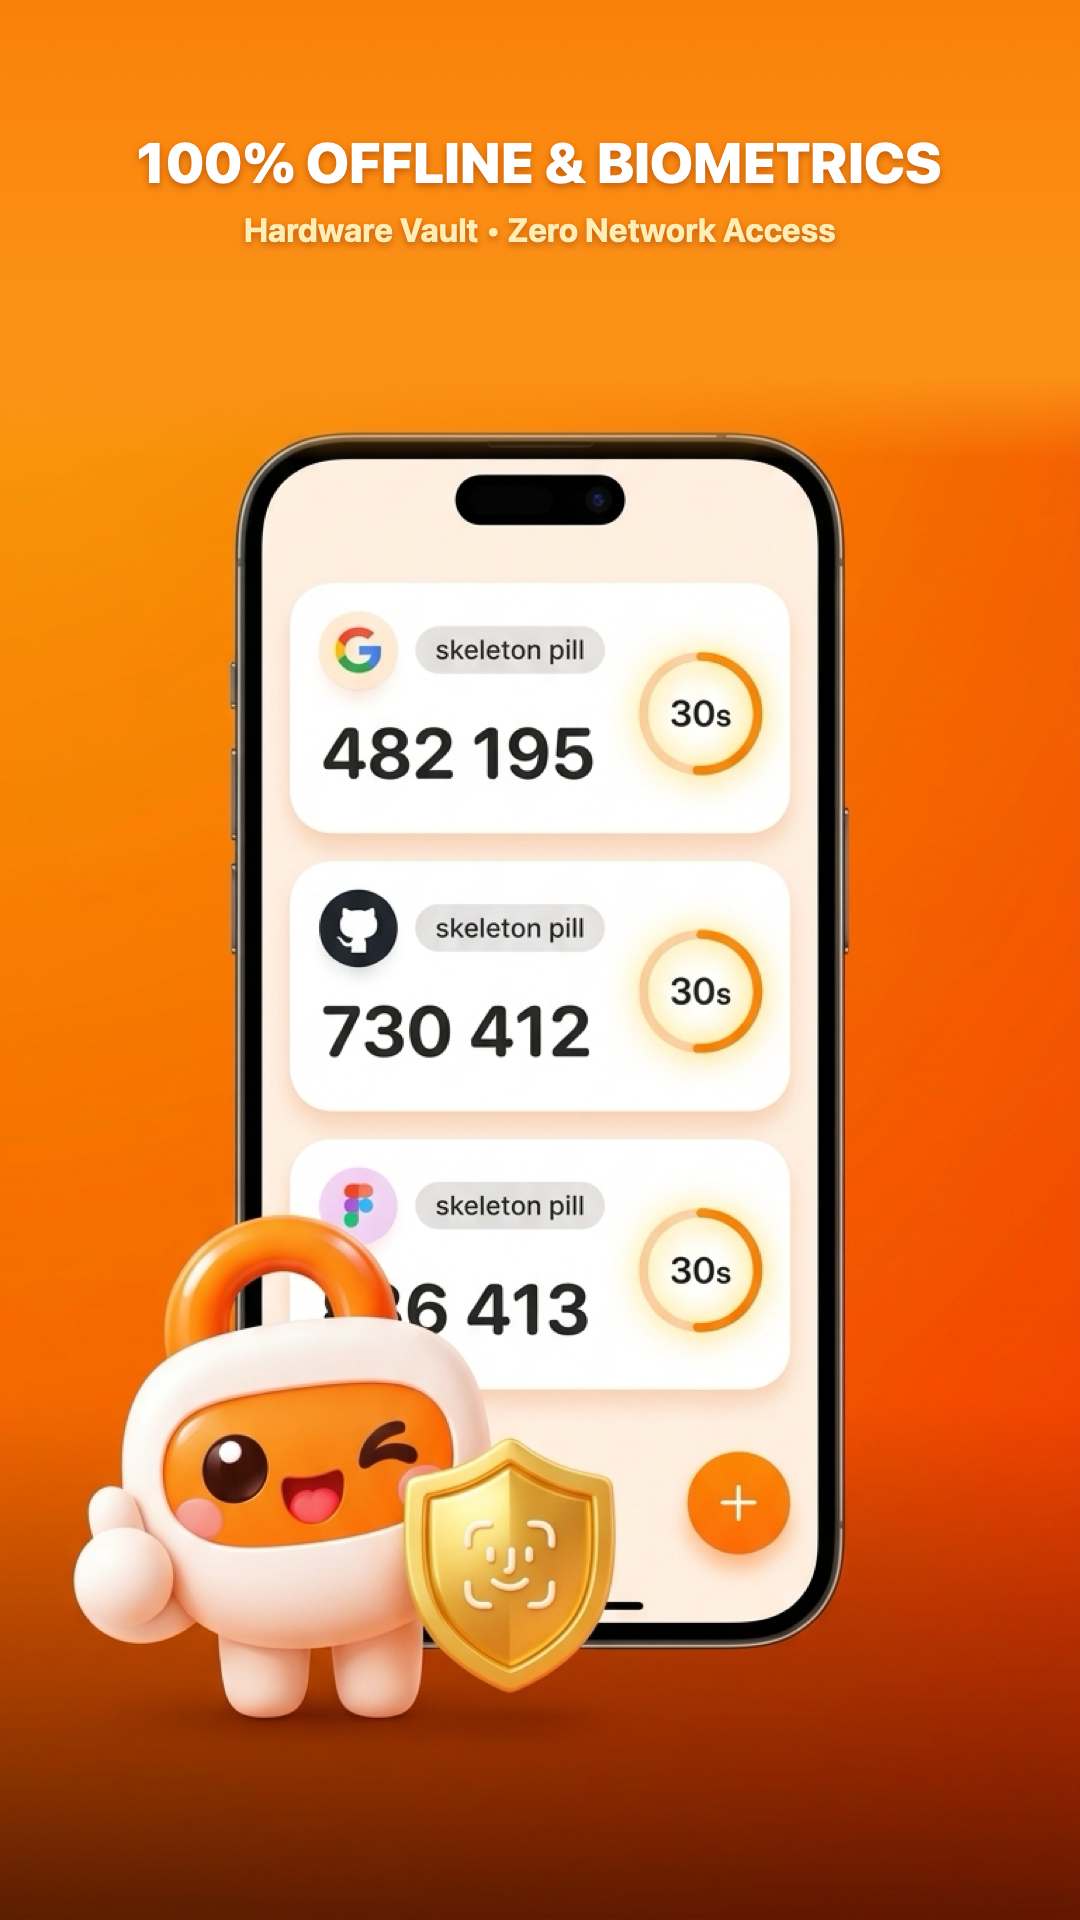
- 0 Network Requests: The application cannot establish outbound connections to any cloud server, including KD Labs.
- 0 Telemetry SDKs: No Firebase Analytics, no Facebook trackers, no behavioral tracking frameworks.
- 0 Cloud Leakage Risk: Your cryptographic secret keys and generated OTP tokens never physically leave your handheld device.
This means you can rely on Simple OTP in complete isolation—whether in Airplane Mode, in remote off-grid locations, or in high-security air-gapped environments.
3. Hardware Vault Enclave: AES-256-GCM & PBKDF2
Operating offline does not mean compromising cryptographic rigor. On the contrary, Simple OTP adheres to enterprise-tier cryptographic specifications:
Hardware-Backed Security (Keystore & Keychain)
Master Vault Keys (MVK) are generated and shielded directly within physical cryptographic chips (Android Keystore on Android and iOS Keychain on Apple devices). Even in device compromise scenarios (root or jailbreak), extracting keys from the secure hardware enclave remains virtually impossible.
AES-256-GCM & PBKDF2 Key Derivation
All local secret token databases are encrypted via AES-256-GCM (Galois/Counter Mode), providing both high confidentiality and cryptographic authenticity verification. Master derivation employs PBKDF2 with 100,000 hash iterations combined with cryptographically secure random salts to withstand brute-force attacks.
Full International Standards Compliance
Simple OTP natively implements:
- RFC 6238: Time-based One-Time Password algorithm (TOTP).
- RFC 4226: HMAC-based One-Time Password algorithm (HOTP).
- Comprehensive hash suite: SHA-1, SHA-256, and SHA-512 with configurable 6 or 8-digit token lengths.
4. Multi-Channel Ingestion & FLAG_SECURE Shield
Fortified security should never come at the expense of user delight. Simple OTP supports frictionless token imports:
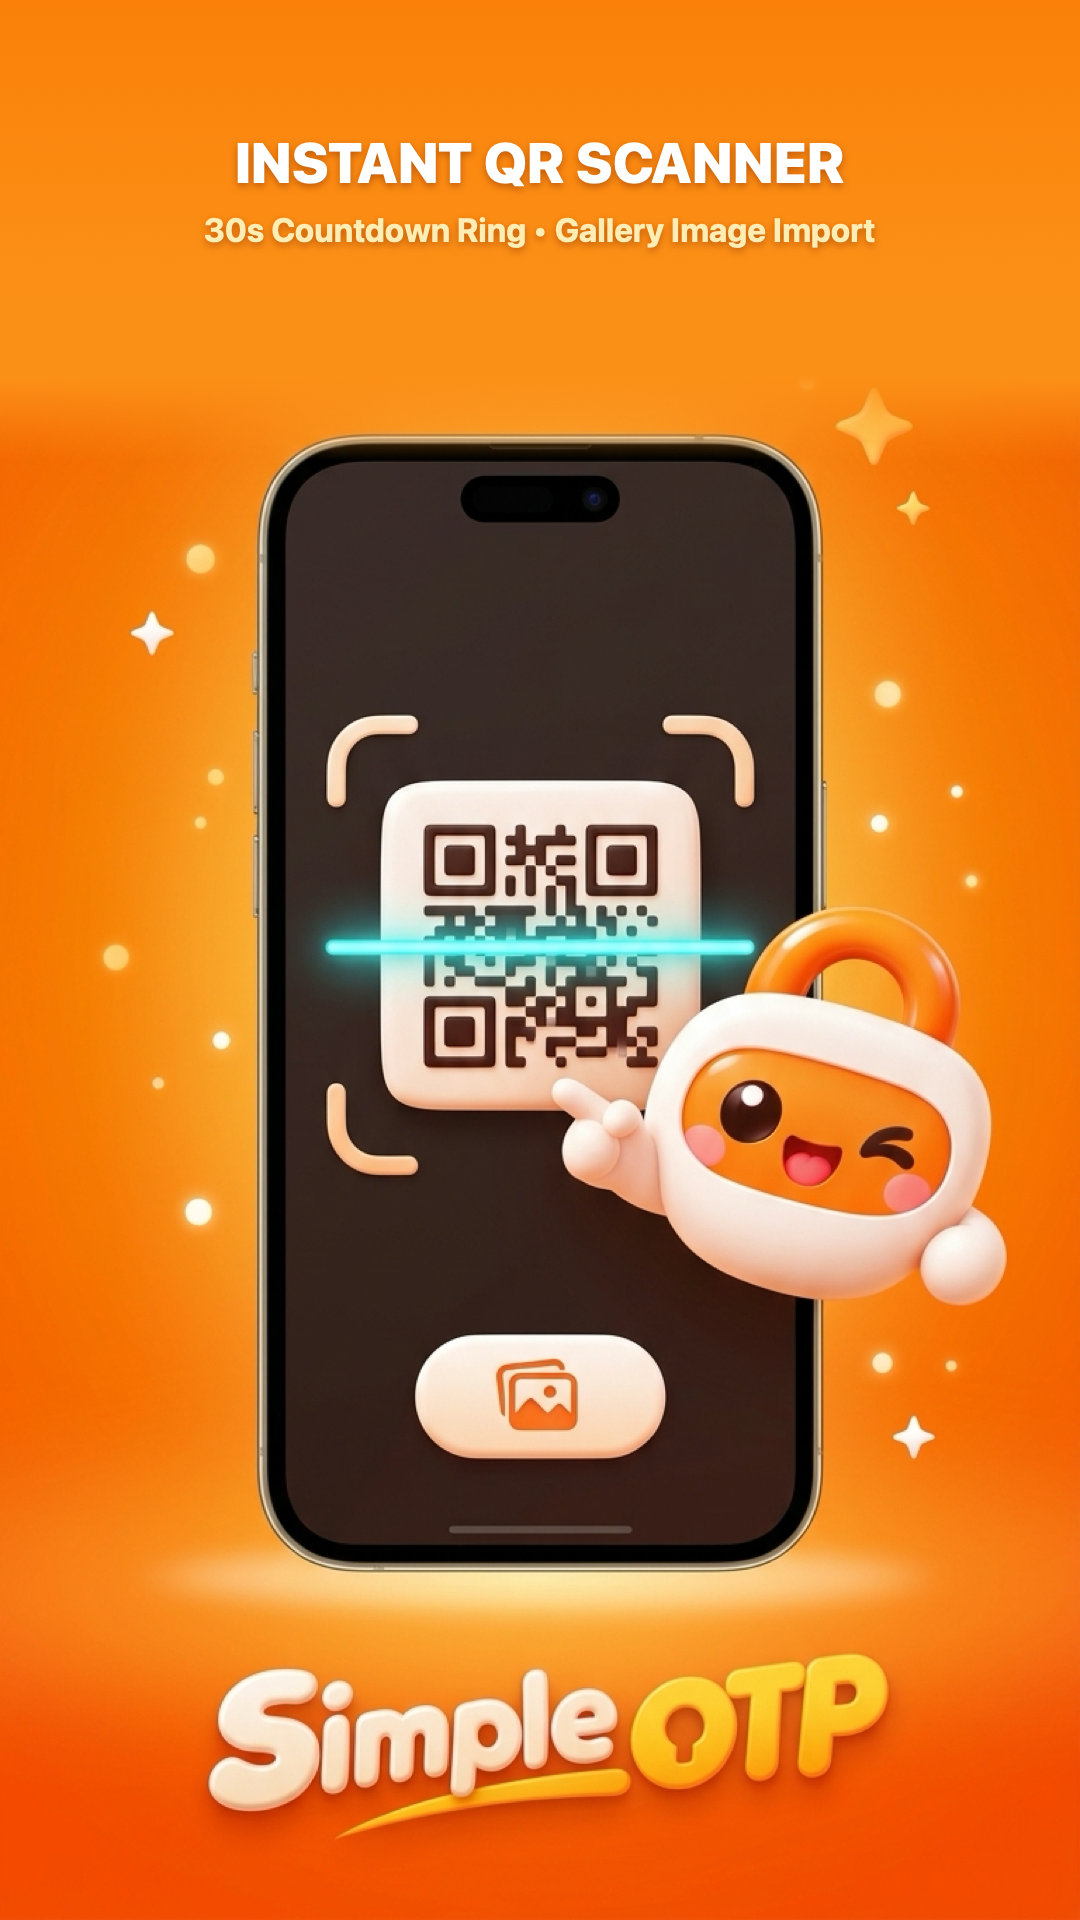
- Live Camera QR Scanning: Instant recognition for tokens from Google, GitHub, Microsoft, AWS, Binance, and more.
- Gallery Photo Scanning: Seamlessly decodes QR codes from saved screenshots.
- Clipboard Detection: Automatically recognizes standard
otpauth://URI strings upon copy. - Manual Entry: For air-gapped systems providing plain text base32 secret keys.
Furthermore, the app engages system-level FLAG_SECURE, preventing unauthorized background screen capture or spyware screen recording while OTP tokens are visible.
5. Delightful Security Companions: Warmth Meets Cryptography
Who decreed that digital cryptography must remain cold and intimidating?
Simple OTP introduces an expressive squad of Companion Mascots:
- Bé Khóa (Lock-bot): A resilient padlock robot who beams with joy whenever you copy a token safely.
- Cipher Cat: A watchful crypto feline guarding your secrets with meticulous care.
- Byte Dog & Shield Bunny: Loyal companions who react playfully to your everyday interactions and tokens.
6. Password-Encrypted Backups (.simpleotp)
To safeguard against device loss or facilitate phone migrations, Simple OTP includes a sovereign offline backup mechanism:
- All token records export into a structured file bearing the
.simpleotpextension. - This file is fortified with AES-256-GCM encryption using a master passphrase chosen solely by you.
- Store your
.simpleotpbackup on an external SD card, flash drive, or transfer it across devices knowing it cannot be inspected without your personal decryption passphrase.
7. Open-Source Transparency under MIT License
In cryptographic software, trust cannot be demanded through marketing copy; it must be proven in the source code.
The complete codebase of Simple OTP is public and transparent under the permissive MIT License:
- GitHub Repository: github.com/001123/simple-otp
- Independent security researchers, developers, and users worldwide are invited to inspect, verify, and audit every line of code.
Looking Ahead
Simple OTP is more than a standard 2FA utility. It stands as KD Labs’ manifesto for mindful software development: minimalist, respectful of user sovereignty, completely private, and timeless.
The app is currently undergoing final quality assurance and will be available soon on the Google Play Store. Stay tuned and experience calm, secure digital peace with Simple OTP!